¿Qué es el marco OSINT y cómo funciona?
Discover the power of the OSINT framework, a useful tool in the landscape of intelligence gathering in our digital era. This guide cuts through the complexity, offering you a clear pathway to explore publicly available data across diverse sectors for security, strategic planning, or research purposes. Learn how to seamlessly integrate these tools into your own analysis.
Key Takeaways
- The OSINT Framework provides a structured approach to gathering publicly available information, expanding in scope due to the internet and digital communications, and offering tools and techniques for open-source data analysis.
- Herramientas OSINT Dentro del marco se permite la recopilación efectiva de datos de diversas fuentes en línea, incluyendo redes sociales y motores de búsqueda. También se extienden a explorar la Deep y la Dark Sitio web, ofreciendo perspectivas en múltiples sectores.
- Ethical considerations in OSINT gathering are crucial, requiring adherence to legal standards such as GDPR and the ethical collection of data, while respecting terms of service and maintaining transparency.
Visión general del marco OSINT
Open-source intelligence (OSINT) involves gathering publicly accessible data from sources like:
- News articles
- Social media posts
- Government reports
- Online forums
- Other OSINT resources
The concept of OSINT originated in military intelligence settings where it was used for espionage and strategic intelligence through media like newspapers and radio broadcasts.
With the growth of the internet and digital communications, the scope and impact of OSINT have significantly expanded. The OSINT Framework provides a structured method for performing open-source intelligence tasks, benefiting security researchers, government agencies, and cybersecurity professionals in information gathering.
¿Para qué se emplea el marco OSINT?
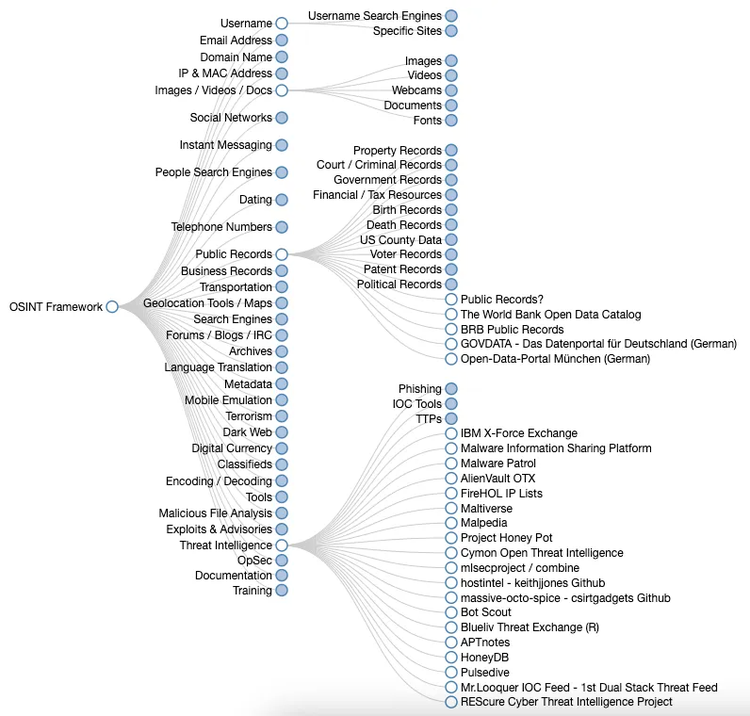
Available via its official website, the main function of the OSINT Framework is to compile publicly available information from multiple online sources. Users can navigate by clicking on categories related to their investigation, such as Username, Email Address, or Domain Name, to view a list of relevant tools and access them directly for their research.
Structured with a systematic methodology, the OSINT Framework categorizes gathered information according to:
- Source
- Relevance
- Type
- Contexto
En esencia, el Marco OSINT se centra en emplear herramientas y recursos gratis de OSINT para ayudar a los usuarios a recopilar información valiosa de la vasta cantidad de datos públicos en línea. Ofrece una variedad de herramientas y técnicas para el análisis de datos de código abierto.
Herramientas clave de OSINT y técnicas de recopilación de datos
The OSINT Framework, besides being an exhaustive source for data collection on multiple targets, can also function as a cybersecurity checklist for scrutinizing individuals or corporations. Tools like Shodan are used to find intelligence about devices and vulnerabilities, while Spyse collects data on websites, their owners, and associated servers.
TheHarvester searches for relevant information from public sources like search engines and social media platforms, displaying results including email addresses and social media profiles. Specialized tools like Spiderfoot integrate with multiple data sources for free and are easily accessible via platforms like GitHub. These tools and resources aid in obtaining real-time insights into current events, incidents, and trends to enhance situational awareness.
Search Engines and Directories
Search engines are crucial in the realm of OSINT. According to Statcounter, Baidu, owns a 61% market share in China, and Yandex, commanding over 71% of the Russian desktop search market (source: Statista), are essential for OSINT due to their widespread use. These search engines provide a wealth of localized data that can be leveraged for intelligence gathering.
Además, motores de búsqueda específicos de región como Naver en Corea del Sur y Seznam en la República Checa son especialmente útiles para OSINT, proporcionando resultados de búsqueda localizados y personalizados relevantes para sus respectivas áreas. Los motores de búsqueda centrados en la privacidad como DuckDuckGo también son vitales para las búsquedas OSINT, donde los usuarios requieren búsquedas que no están vinculadas a su historial personal de navegación.
Social Media Monitoring
Social media platforms offer a wealth of data for OSINT. Social Mention, a social media search engine, focuses on specific terms and phrases, pulling results from over one hundred social media platforms. This tool allows analysts to gather a vast amount of information from various platforms, enhancing their ability to gather comprehensive data.
Trendsmap se emplea para analizar las palabras clave y los hashtags de tendencia en Twitter, e incluye un estable sistema de detección de spam para garantizar la autenticidad de las tendencias. Del mismo modo, Hashatit permite a los usuarios buscar y analizar hashtags activos en múltiples plataformas de redes sociales, recopilando publicaciones relacionadas en un solo lugar. Estas herramientas refuerzan considerablemente las capacidades de monitorización de las redes sociales, un aspecto importante de la inteligencia de fuentes abiertas (OSINT).
Deep and Dark Web Exploration
The Deep and Dark Web, often seen as the internet’s underbelly, holds valuable information for OSINT. This part of the web is not indexed by conventional search engines and requires specialized tools like the Tor browser for access. TorBot, a Python-based OSINT tool for the dark web, is designed to crawl and index .onion sites, returning information such as page titles, addresses, and descriptions, while storing the results in a JSON format.
Incorporating dark web monitoring is essential for a comprehensive OSINT strategy, enabling ongoing surveillance of illicit activities. Maltego, used in conjunction with Elasticsearch and Kibana, allows analysts to visualize and analyze dark web data through storage and complex query execution. Ahmia.fi serves as a deep web search engine that gathers .onion URLs from the Tor network, creating a significant index of such content. These tools and resources assist in probing the deep and dark web, a key component of OSINT.
Casos de uso avanzados y aplicaciones sectoriales
Delving deeper into the OSINT framework reveals advanced techniques furnishing valuable insights across multiple sectors. Industrial control systems (ICS), critical components of operational infrastructure, can be analyzed through advanced OSINT techniques, offering insights into companies, infrastructure, and technology relevant to the industrial sector. For a deeper understanding of how these and other intelligence insights can enhance the security and resilience of critical infrastructure, visit Recorded Future's discussion on attack surface intelligence for critical infrastructure.
The intelligence cycle, including the following stages, is vital in applying OSINT techniques alongside traditional intelligence gathering methods to generate actionable intelligence on industrial control systems:
- Preparation
- Collection
- Processing
- Analysis
- Dissemination
Técnicas como el uso de operadores de búsqueda avanzados, herramientas de extracción de datos sitio web y el análisis de direcciones IP permiten a los analistas identificar posibles amenazas emergentes y descubrir información detallada sobre equipos industriales, vulnerabilidades e incidentes de seguridad relacionados con los sistemas de control industrial.
Furthermore, analysis of documents like patent filings, technical manuals, and industry reports, coupled with data analysis tools, is instrumental in identifying trends, vulnerabilities, and operational insights about industrial control systems.
Aplicaciones OSINT en diferentes sectores
The wide-ranging applicability across diverse fields signifies the versatility of OSINT. It enables organizations and individuals to gather information in real-time, supporting informed decision-making and providing early warnings of potential threats. Businesses leverage OSINT for gaining insights into competitor activities and market trends, which are essential for maintaining a competitive edge.
Investments in AI and machine learning have advanced the scope of OSINT applications, enabling large-scale intelligence collection and situational awareness. As a result, OSINT is increasingly being adopted across various fields, demonstrating its broad utility in different sectors.
Government and Law Enforcement
OSINT es una herramienta ampliamente empleada en las operaciones de agencias gubernamentales y fuerzas de seguridad. Agencias como la Agencia Nacional contra el Crimen del Reino Unido y el FBI de EE . UU. emplean OSINT para:
- Investigate large-scale organized crime
- Investigate international criminal activities
- Apprehend offenders
- Disrupt crimes, including different types of cybercrime, fraud, violent crimes, and terrorism
OSINT enables law enforcement agencies to effectively carry out their duties and maintain public safety.
Además de combatir a los ciberdelincuentes, OSINT desempeña un papel fundamental en la identificación y comprensión de las actividades de grupos terroristas y extremistas, ayudando a predecir y prevenir ataques. Los datos disponibles públicamente analizados a través de OSINT ayudan a las agencias gubernamentales a preparar y responder ante desastres naturales y crisis de salud pública. Esta amplia gama de aplicaciones demuestra el inmenso valor de la OSINT para el gobierno y las agencias de seguridad.
Corporate Security and Business Strategy
Within the corporate sphere, OSINT proves valuable in ensuring security and gaining a competitive advantage. Businesses leverage OSINT for insights into competitor activities and market trends, which are essential for maintaining a competitive edge. OSINT facilitates timely detection of sensitive data exposure, allowing cybersecurity teams to implement quick responses including security patches and containment measures.
By uncovering publicly accessible digital footprints, OSINT techniques are essential in conducting thorough cybersecurity assessments and intelligence gathering. The integration of OSINT data with broader cybersecurity intelligence processes allows for a comprehensive analysis of security risks and strategic, informed decision-making.
Ethical Considerations in OSINT Gathering
A pesar de la gran cantidad de información que ofrece OSINT, seguir las directrices éticas durante su recopilación sigue siendo fundamental. El Marco OSINT enfatiza la importancia de cumplir con las directrices éticas y cumplir con las leyes pertinentes, como el Reglamento General de Protección de Datos (RGPD) para el manejo de datos personales en Europa. En países concretos como Alemania, los analistas de la OSINT deben demostrar un 'interés legítimo' en sus investigaciones para garantizar el cumplimiento de los estándares legales.
Ethical OSINT gathering involves respecting terms of service, refraining from using fake identities or hacking, and maintaining transparency about intentions with information collection. Documenting actions during OSINT investigations is essential for demonstrating accountability and ethical decision-making in line with regulatory and law enforcement guidelines.
Uso de OSINT con estrategias de ciberseguridad más amplias
OSINT is not a standalone tool; it can be amalgamated with other cybersecurity practices, such as information security point measures, to yield superior results. Open Source Intelligence (OSINT) is a critical tool used by cybersecurity professionals to identify compromised credentials, potential vulnerabilities within organizations, and overall cyber risks. It facilitates timely detection of sensitive data exposure, allowing cybersecurity teams to implement quick responses including security patches and containment measures.
OSINT complements internal cybersecurity measures by enriching the telemetry of security systems and providing penetration testers with actionable data on vulnerabilities. To transform OSINT into a practical asset for cybersecurity, raw data must be curated to ensure it possesses attributes like timeliness, verifiability, and a low false positive rate. Utilizing OSINT resources effectively can greatly enhance the overall security posture of an organization, and incorporating threat intelligence can further strengthen this approach.
Incorporating new tool suggestions and exploring various tools expand the toolkit available for cybersecurity teams and OSINT researchers, offering more data for thorough analysis. This approach proves invaluable not only for cyber crime investigations but also for business intelligence. Moreover, OSINT's utility extends beyond cybersecurity, serving as an essential asset for news reporters and other professionals seeking to gain insights into current events. This broad applicability underscores OSINT's value across different domains, making it an indispensable tool in the digital age.
Contribuyendo y evolucionando el marco OSINT
The evolution of the OSINT Framework hinges on continuous learning and improvement, with community contributions significantly influencing this process. Individuals can contribute to the OSINT Framework by ensuring their suggested resources are publicly accessible and consulting the development guide for how to add content.
New resources can be suggested by first updating the ‘arf.json’ file with the required format, then submitting a pull request on the OSINT Framework’s GitHub for review. The creator of the OSINT Framework encourages diverse community contributions, even from those outside information security, by adding new search engines or modules, thereby diversifying the available tools.
Take the OSINT intelligence gathering to the next level
For organizations looking to deepen their intelligence capabilities and stay ahead in the ever-evolving digital landscape, Recorded Future offers cutting-edge solutions that seamlessly integrate with the principles and tools outlined in the OSINT Framework. Our platform leverages the vast potential of OSINT, combined with advanced analytics, to provide actionable intelligence that empowers your decision-making processes. Book your demo today!
FAQs
¿Qué son las herramientas del Marco OSINT?
Un marco OSINT es una herramienta para recopilar información de recursos gratis que ayuda a encontrar recursos OSINT. Su objetivo es proporcionar acceso a la información gratis, aunque algunos sitios pueden requerir registro u ofrecer datos adicionales a cambio de una tarifa.
¿Cuál es un ejemplo del Marco OSINT en uso?
Yes, the OSINT framework is legal because it only uses information available from public sources, making it completely legal and ethical to use.
¿Cómo emplear el marco OSINT?
Yes, OSINT can be free to use, as there are various platforms and tools available at no cost, such as Maltego or basic web search tools. While some sources may require a subscription, most tools offer free versions.
What is the best OSINT?
Las mejores herramientas OSINT incluyen Google Dorks, Sherlock, Holehe, Shodan, The Harvard, PimEyes y WHOIS Lookup, que pueden ayudarte a buscar información de forma eficaz.
What is OSINT and why is it important?
OSINT, or open-source intelligence, is important as it allows organizations and individuals to gather real-time information from publicly available sources, supporting informed decision-making and providing early warnings of potential threats.
Esteban Borges
Esteban is a seasoned security researcher and IT professional with over 20 years of experience, specializing in hardening systems and networks, leading blue team operations, and conducting thorough attack surface analysis to bolster cybersecurity defenses. He's also a skilled marketing expert, specializing in content strategy, technical SEO, and conversion rate optimization. His career includes roles as Security Researcher and Head of Marketing at SecurityTrails, before joining the team at Recorded Future.