What are Threat Intelligence Feeds?
What are threat intelligence feeds, and why do they matter for your cyber defenses? These real-time data streams are vital in pre-empting cyber attacks, offering the latest information on potential threats.
By informing you of dangers before they strike, threat intelligence feeds are your first line of digital defense. This article will explore their types, impact, and how they integrate with your cybersecurity measures.
Key Takeaways
- Threat intelligence feeds provide real-time data on cyber threats, enabling security teams to quickly identify, understand, and mitigate threats by offering actionable intelligence including IOCs, TTPs, and context for the most pressing issues.
- Through proactive threat detection and response, threat intelligence feeds are integral in enhancing an organization’s security posture, ensuring early identification and mitigation of threats, which helps in developing refined defensive strategies and improving decision-making.
- Effective use of threat intelligence feeds involves integration with an organization’s existing security tools and infrastructure, prioritization of threats for efficient resource allocation, and continuous evaluation to maintain quality, reliability, and cost-effectiveness.
What are Threat Intelligence Feeds?
Threat intelligence feeds provide a constant flow of data that offers up-to-the-minute details about cyber threats worldwide. These feeds gather information from various sources, including security experts, government agencies, and open-source intelligence.
The data is processed and analyzed, transforming raw information into actionable threat intelligence. This actionable intelligence includes indicators of compromise (IOCs), tactics, techniques, and procedures (TTPs) used by threat actors. This threat intel is invaluable to security teams, enabling them to identify, understand, and mitigate threats swiftly.
Además, los feeds de inteligencia sobre amenazas desempeñan un papel fundamental al proporcionar flujos automatizados de información útil sobre amenazas, incluyendo indicadores de compromiso (IoC), información sobre actores amenazantes, dominios y direcciones IP sospechosos, hashes de malware y más, que son esenciales para mantener la postura de seguridad de una organización.
TechTarget highlights the value of threat intel feeds by stating:
And according to Cloudflare they are used to:
The effectiveness and utility of threat intelligence feeds rely on the context they offer. Without context, the data might seem overwhelming and challenging to interpret. However, with the right context, security teams can focus on the most pressing threats, thus enhancing their response time and efficiency.
Key Components of Effective Threat Intelligence Feeds
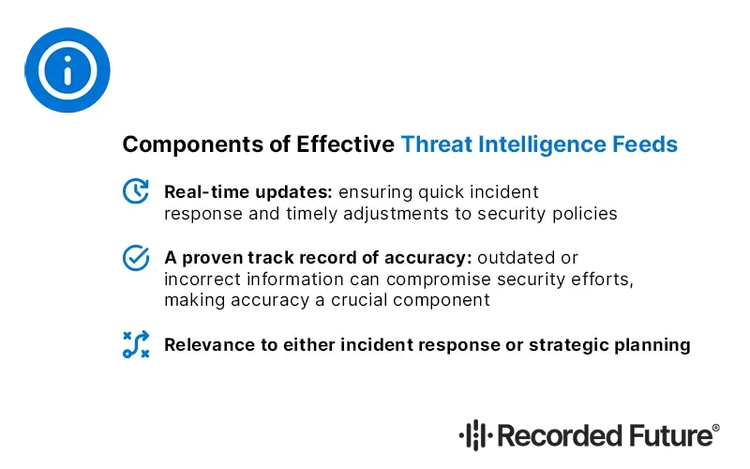
Effective threat intelligence feeds share common attributes. They offer:
- Real-time updates: ensuring quick incident response and timely adjustments to security policies
- A proven track record of accuracy: outdated or incorrect information can compromise security efforts, making accuracy a crucial component
- Relevance to either incident response or strategic planning: often determined by whether it offers real-time insights versus long-term trends.
Contextual analysis in threat intelligence feeds is another key component. It provides insights into the origins and impact of threats, aiding security teams in crafting appropriate response and mitigation strategies. Furthermore, effective threat intel feeds must present relevant data, streamlining security investigation and response. This curation saves valuable time for security teams.
Finally, the quality and industry relevance of the sources contributing to threat intelligence feeds are vital to the utility and effectiveness of the received intelligence.
Types of Threat Intelligence Feeds
Threat intelligence feeds are primarily categorized into three types:
- Commercial feeds: These gather anonymized metadata from customers and analyze it to provide threat intelligence. They often come from reputable cybersecurity firms and provide comprehensive coverage of the threat landscape.
- Open-source feeds: These are publicly available sources of threat intelligence, such as public forums, blogs, newsletters (like Cyber Daily), social media, and even threat intelligence browser extensions. They can provide valuable information but may require more manual threat intelligence analysis.
- Fuentes basadas en la comunidad: Se trata de esfuerzos colaborativos en los que individuos y organizaciones comparten inteligencia de amenazas entre sí. Pueden ser valiosos para información específica o de amenazas específicas. Algunos ejemplos incluyen Google SafeBrowsing, o VirusTotal.
- Government and Non-Governmental Organization (NGO) Threat Intelligence Feeds: governments and NGOs provide threat intelligence feeds, sometimes for free or at a cost, which include platforms for sharing threat data among entities, like the Department of Homeland Security's Automated Indicator Sharing or the FBI's InfraGard project. These feeds are valuable for staying informed about cyber threats but relying solely on them can result in a limited perspective of the threat landscape.
Each type has its unique characteristics and advantages.
The Importance of Cyber Threat Intelligence Feeds
Threat intelligence feeds play a pivotal role in transforming reactive security efforts into proactive ones. By providing real-time insights into potential cyberattacks, these feeds enable early identification and response, thereby preventing breaches.
The information these feeds offer enhances the ability of security teams to:
- Develop refined defensive strategies
- Gain insights into the tactics, techniques, and procedures of adversaries
- Create a clear picture of the threat landscape
Furthermore, threat feeds empower security teams to make faster and more informed decisions, backed by data. This data-driven approach significantly bolsters an organization’s cybersecurity. With a broader understanding of the cyber threat landscape, organizations can better assess and prioritize the risks they face, ensuring resources are allocated to the most pressing threats.
Enhancing Security Posture
One of the significant benefits of threat feeds is their capacity to enhance an organization’s security posture. By offering actionable intelligence, these feeds empower security teams to gain a deeper understanding of threats and fine-tune their protection strategies. However, to fully harness the power of these feeds, organizations need to evaluate their existing security posture, understand their industry’s inherent risks, and consider the compatibility of the feeds with their current security tools.
An effective way to improve response times to cyber threats is through security automation. By automating responses to alerts provided by threat intel feeds, organizations can act swiftly against cyber threats, thereby preventing potential data breaches.
Proactive Threat Detection and Response
Threat intelligence feeds are the cornerstone of proactive threat detection and response. They enable security teams to:
- Address security threats before they escalate into major issues
- Proactively identify and mitigate threats
- Understand the tactics used by threat actors
- Guide security policies
- Identify vulnerabilities
- Inform access permissions and security updates
Cybersecurity professionals utilize threat intel to stay one step ahead of potential cybersecurity threats and protect their systems and data.
Threat intelligence feeds provide essential information on emerging threats and share best practices for responding, which significantly supports incident response efforts. With real-time threat data, security teams are promptly informed of potential issues, reducing the likelihood and costs of significant data breaches.
Enter Threat Intelligence Data
Leveraging threat intelligence data effectively is a critical process that involves integrating feeds with existing security tools and prioritizing threats for efficient resource allocation. The actionability of threat intelligence data is determined by the level of context provided and its capacity to be readily used in correlation with other security tools and platforms.
Curated threat intel feeds compile data from various sources, including private and public repositories, allowing security teams to save time and enhance their investigative and response actions.
Integration with Security Tools
Integrating threat intel feeds with existing security tools can:
- Extend these tools’ useful life
- Improve their return on investment
- Minimize alert fatigue in security operations centers
- Provide filtered, prioritized alerts for better management
- Incorporate both third-party and local threat intelligence into existing security solutions
- Expand the slate of covered threats
- Enhance the identification and blocking of threats
Advanced Threat Intelligence (ATI) tools that employ algorithms to rapidly identify anomalies often assist in this integration. The process is further supported by the availability of integrations such as APIs or native third-party integrations that simplify ingest into the current security infrastructure.
Prioritizing Threats and Allocating Resources
Threat intelligence data facilitates the creation of metrics that help organizations quantify and rank threats. This process effectively prioritizes critical vulnerabilities, ensuring resources are allocated to the most pressing threats. Classifying high-risk activities and incidents using threat intelligence data supports the strategic allocation of cybersecurity resources and enhances strategic threat intelligence.
Incorporating threat intelligence into incident response mechanisms allows organizations to:
- Respond to threats both swiftly and strategically
- Strategize the deployment of rules and Indicators of Compromise (IoCs) in Security Operations Centers (SOCs)
- Ensure that rules and IoCs are constantly updated and fine-tuned to keep up with evolving threats.
Threat intelligence feeds also provide vital data on vulnerabilities, exploits, and attack methods, which can be prioritized to improve patch management efforts within an organization.
How can I choose the right threat intelligence feed for my organization?
Choosing the right threat intelligence feed for your organization is a critical decision. It involves assessing quality, reliability, cost, and value, as well as considering the organization’s specific needs and budget constraints.
Criteria for evaluating threat intelligence feeds include the ability to:
- update data in real time
- access to multiple data sources
- and the speed and format of the feed’s dissemination
To enhance the value of threat intelligence within an organization, it is important to evaluate the unique data provided by each feed to prevent overlapping information and redundancy.
Integrating threat intelligence feeds requires an analysis of their relevance to the organization’s threat landscape to ensure that they are aligned with the specific threats the organization is facing.
Assessing Quality and Reliability
The quality and reliability of threat intelligence feeds are evaluated based on trustworthiness and variety of information sources, range and depth of coverage, and if they offer contextual analysis and dashboarding capabilities. To ensure threat intelligence feeds are truly actionable, organizations should routinely monitor data reliability and confirm that the feed’s data sources are relevant to their industry’s specific threats.
Selecting high-fidelity threat intelligence feeds requires assessing vendors for their credibility and the historical reliability of their feeds. This assessment can be measured against their success rate in correlating with previous incidents.
Balancing Cost and Value
While many threat intelligence feeds are free to use, commercial feeds typically require an annual subscription that can range from a few thousand dollars to over $100,000 per year. Organizations should align their choice of threat intelligence feeds with the budget they have available for cybersecurity efforts.
To ensure cost-effectiveness, organizations need to evaluate whether a threat intelligence feed provides unique value that justifies its cost and avoids redundancy with other feeds.
Top Threat Intelligence Feeds to Consider
When it comes to threat intelligence feeds, there are numerous options to consider.
- El Internet Storm Center: es reconocido por ofrecer explicaciones exhaustivas sobre amenazas.
- Spamhaus: specializes in email security and anti-spam, offering robust solutions in that domain.
- URLhaus: primarily addresses IP address and domain name anomalies and is best suited for network operators, ISPs, CERTs, and domain registries.
- AlienVault OTX feeds: are accessible through detailed dashboards, which provide Pulses to summarize threats and display various indicators of compromise.
- Recorded Future Threat Intelligence: while not a traditional feed, our intelligence cloud platform represents a significant advancement in threat intelligence. We automate the curation of intelligence feeds, streamlining the process to help you identify and prioritize threats more efficiently. Keep reading to learn more.
Contextual Threat Intelligence for Security Teams
When they first appeared, threat intelligence feeds constituted a huge leap forward, enabling security professionals to manage higher levels of relevant information than ever before. As the cyber threat intelligence cycle evolved, it became apparent that the abundance of free feeds in particular became “noisy" and filled with errors and false positives. These issues, coupled with the sheer volume of data available, started to pose problems.
Instead of viewing dozens of feeds separately, using a threat intelligence platform not only combines them all but also curates and compares the internal telemetry, generating customized alerts for your incident response and threat intelligence team.
The most powerful intelligence platforms, like the Recorded Future Intelligence Cloud, automatically curate intelligence feeds, sifting through data to identify and prioritize threat intelligence for your organization to action.
Implementing Threat Intelligence Feeds in Your Organization
Implementing threat intelligence feeds in an organization is a critical step towards enhancing cybersecurity. It involves integrating with the existing infrastructure, training and awareness, and ongoing evaluation and optimization. Before the implementation, it’s essential to assess the organization’s cybersecurity infrastructure and gain executive support.
Ensure that the current cybersecurity solutions, such as SIEM or EDR systems, can integrate with the selected threat intelligence feeds for proper functionality. Develop and deliver comprehensive training programs to educate staff on the operational procedures and benefits of threat intelligence feeds. Lastly, establish protocols for regular review and optimization of threat intelligence feeds to maintain their relevance and effectiveness.
Identify key stakeholders within the organization and involve them in the planning for adopting threat intelligence feeds.
Integration with Existing Infrastructure
Integrating threat intelligence feeds with existing tools can extend these tools’ useful life and improve their return on investment. Organizations should combine third-party threat intelligence with their own local intelligence sources for a more comprehensive coverage.
Training and Awareness
Training security teams is a critical component of leveraging threat intelligence feeds, ensuring they understand how to employ this information effectively. Security personnel must be trained to differentiate and respond efficiently to high-priority alerts to take timely action against critical threats.
Proper training includes measures to manage the volume of alerts and prevent burnout from SOC alert fatigue by focusing on significant and actionable alerts.
Para mejorar aún más las capacidades de su equipo, considere inscribir en Universidad del Futuro Grabada. Nuestro curso gratis de Fundamentos de Inteligencia está diseñado para dotar a los participantes de las habilidades necesarias para analizar y actuar eficazmente en función de la inteligencia sobre amenazas, transformando la información en conocimientos prácticos y defensas estratégicas.
Frequently Asked Questions
How does a threat intelligence feed work?
A threat intelligence feed gathers information from different sources, processes, and analyzes it to provide actionable intelligence for cybersecurity purposes.
What are the benefits of using threat intelligence feeds?
Using threat intelligence feeds allows organizations to proactively identify and respond to cyber threats, enhance their security posture, and make informed decisions regarding cybersecurity.
How can an organization implement a threat intelligence feed effectively?
To implement a threat intelligence feed effectively, an organization should integrate the feed with existing infrastructure, provide comprehensive staff training, and establish protocols for regular review and optimization of the feed. This will ensure a proactive and informed approach to cybersecurity.
What’s the difference between Threat Feeds vs Threat Intel Feeds?
Threat Feeds generally refer to raw data on emerging threats, whereas Threat Intel Feeds include analyzed data that offers actionable intelligence, crucial for crafting effective security strategies. Threat Intel Feeds produce refined reports that help in understanding the tactics and behaviors of threat actors.
Summary
To sum it up, threat intelligence feeds provide real-time insights into potential threats, enabling organizations to shift from a reactive to proactive approach. Implementing the right threat intelligence feed involves careful evaluation and selection, as well as effective integration with the existing infrastructure.
Go Beyond Manual Feeds: Unlock Advanced Threat Intelligence Automation
Level up your organization's security by fully integrating Recorded Future's Threat Intelligence solutions into your cybersecurity program. To see how our platform can transform your threat detection and response strategies, book a demo with us today.
Esteban Borges
Esteban is a seasoned security researcher and IT professional with over 20 years of experience, specializing in hardening systems and networks, leading blue team operations, and conducting thorough attack surface analysis to bolster cybersecurity defenses. He's also a skilled marketing expert, specializing in content strategy, technical SEO, and conversion rate optimization. His career includes roles as Security Researcher and Head of Marketing at SecurityTrails, before joining the team at Recorded Future.