October 2026 CVE Landscape
In October 2026, Insikt Group® identified 82 high-impact vulnerabilities to prioritize for remediation, 52 of which had a Very Critical Recorded Future Risk Score. This represents a 13% decrease from the 94 vulnerabilities reported in September.
36 of October’s high-impact CVEs were surfaced through the US Cybersecurity and Infrastructure Security Agency (CISA)’s Known Exploited Vulnerabilities (KEV) catalog, 33 were reported in open sources and validated by Insikt Group, and 13 were exclusively surfaced through honeypot data.
The 82 vulnerabilities in this report affected products from 51 vendors, with Citrix and Microsoft together accounting for approximately 15% of the vulnerabilities. The remaining exposure spanned network edge and security management appliances; operating systems and endpoint software; collaboration, content management, and enterprise platforms; and artificial intelligence (AI), developer, and automation tools.
Insikt Group created a Nuclei template to detect the two PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619). Insikt Group also published templates for CVE-2026-87902 (WordPress) and CVE-2026-86124 (AutoAgent). These are available to customers in the Recorded Future Intelligence Operations Platform.
Quick reference: October 2026 vulnerability table
All 69 vulnerabilities below were actively exploited or operationally weaponized in October 2026. This table does not include the 13 CVEs that were exclusively surfaced through honeypot data, which are available to Recorded Future Intelligence Platform customers via the CVE Monthly report. 以下の表には、Insikt Groupが特定した公開PoC(概念実証)の例も示されています。これらの概念実証(PoC)は、正確性や有効性について検証されていません。脆弱性管理チームは、テストを実施する前に、PoC(概念実証)の妥当性を慎重に検証する必要があります。
スコア
表1: List of vulnerabilities that were actively exploited in October 2026 based on Recorded Future data (excluding honeypot-sourced CVEs).
Key trends: October 2026
- PHP2Shell reporting covered confirmed honeypot shell execution, a Fragnesia chain yielding root access on 25 servers, and Potassium-associated payload attempts. Other PHP2Shell activity involved suspected preparations for a North Korean attack, which was assessed with moderate confidence as linked to the Lazarus Group. Other exploitation activity this month included Longlegs deploying Warlock ransomware; ransomware groups exploiting PAN-OS; CL-STA-0954 targeting Fortinet products for data theft; PEERSTITCH deployment; Integrity Technology Group-enabled espionage; CyberXero’s AI-assisted exploitation; and ClingSTUN deployment.
- 37 of the 82 vulnerabilities enabled remote code execution (RCE). Collaboration, content-management, and enterprise platforms were the most affected product type, with 12 vulnerabilities. Microsoft had the largest vendor share, with three vulnerabilities.
- Insikt Group identified public proof-of-concept (PoC) exploits or scanners for 37 of the 82 vulnerabilities in this report.
- The most common weakness class was CWE-78 (OS Command Injection), with eight vulnerabilities, followed by CWE-287 (Improper Authentication), with seven. CWE-22 (Path Traversal) and CWE-77 (Command Injection) each affected six vulnerabilities.
- 10 of the 82 vulnerabilities were at least five years old, and the oldest was approximately 16 years old.
Trend analysis
PHP2Shell exploitation enables root access and internal pivoting
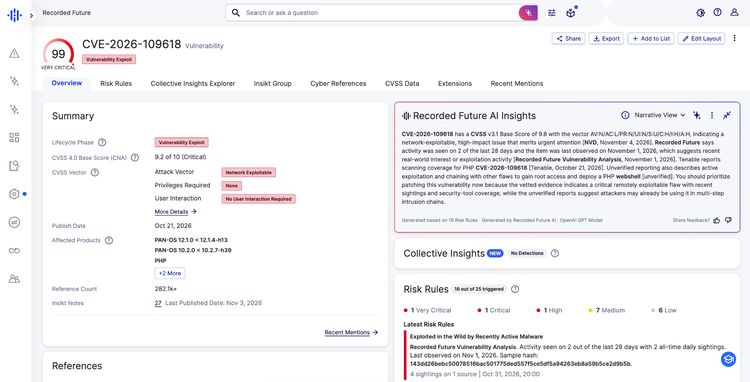
In October, two vulnerabilities in PHP, CVE-2026-109618 and CVE-2026-109619 (collectively referred to as “PHP2Shell”), drew attention from threat actors, who also chained them with CVE-2026-46300, a Linux kernel vulnerability known as Fragnesia. Following their disclosure, Insikt Group published multiple notes and detection rules involving PHP2Shell in October. Highlights from our coverage include:
- Root access and internal pivoting: A TTP Instance detailed a campaign chaining CVE-2026-109618 (PHP) and CVE-2026-109619 (PHP) with CVE-2026-46300 (Linux kernel), also known as Fragnesia. Dream Research reported root access on 25 servers, including systems in a US government-affiliated environment. PHP2Shell provided initial access, and Fragnesia enabled privilege escalation. The actor deployed web shells, stole configurations, credentials, and private keys, and maintained reverse Secure Shell (SSH) tunnels to internal systems, enabling service-account password decryption and Active Directory enumeration. Domain-account creation was attempted but not confirmed.
- Technical analysis and exploit development: A separate TTP Instance explained PHP2Shell’s memory-lifecycle failures enabling unauthenticated remote code execution (RCE), highlighting Apache mod_php exposure and unvalidated early PoCs. Separate TTP Instances covering reports from SOCRadar and AkatsukiLegion described actor-staged exploits, prerequisite checks, and a memory-leak-to-command-execution chain.
- Threat actor pre-positioning: Two other TTP Instances covered PHP2Shell tooling on an extortion actor’s staging server and CYFIRMA’s assessment of suspected North Korean preparations using 21 compromised nodes to check 216 hosts. CYFIRMA assessed a Lazarus Group connection with moderate confidence. Neither earlier shared-hosting intrusions nor attack preparations established a successful PHP2Shell compromise.
- Botnet activity: A TTP Instance covering Arctic Wolf and Cisco Talos described probes and payload-download attempts associated with Potassium, a Mirai-derived botnet. In separate TTP Instances covering Linux bots reported by Joe Security and Nextron Research, Insikt Group corroborated remote-shell, evasion, and denial-of-service capabilities in the former, and PHP2Shell testing, scanning, downloads, and persistence in the latter. These findings did not confirm successful malware delivery through PHP2Shell.
- Detection rule coverage: Insikt Group created Sigma rules for Linux and Windows to detect web or PHP workers spawning shells, including PowerShell, and Suricata and Snort rules for multipart session-ID and upload-progress requests. Network detection requires visible HTTP bodies. Correlate these alerts with process creation, worker errors, and outbound activity because individual matches can be benign.
- Separate PHP vulnerability: A TTP Instance reported on CVE-2026-115560 (PHP), a vulnerability distinct from PHP2Shell that could enable unauthenticated RCE in applications switching session serializers while upload progress is enabled. No in-the-wild exploitation was established at the time of publication. PHP recommended disabling session upload progress pending a separate fix; the initial PHP2Shell patches did not address this vulnerability.
Ransomware and data theft follow exploitation of collaboration and security platforms
A Validated Intelligence Event detailed Longlegs, also known as Storm-2603, exploiting CVE-2025-49704, CVE-2025-49706, CVE-2025-53770, and CVE-2025-53771 (all related to SharePoint Server). Symantec reported that the actor used the ToolShell chain to access critical infrastructure organizations, move laterally, and deploy Warlock ransomware. The intrusion included domain-account privilege changes, credential spraying, and remote-access tunnels. The actor disabled endpoint protections and staged ransomware in a domain replication path, allowing normal replication to propagate the binaries between domain controllers.
A Vulnerability Intelligence note linked exploitation of CVE-2026-0257 (PAN-OS) to Qilin, Settra, and Tarnished Scorpius, which overlaps with activity Recorded Future tracks as INC Ransom. The reporting described the use of BloodHound and SharpHound to examine Active Directory relationships.
A separate Vulnerability Intelligence note described Longlegs exploiting CVE-2025-1055 (K7 Anti-Malware) through the signed K7RKScan driver to terminate protected security processes. Although this activity is also linked to Longlegs, it is separate from the SharePoint exploitation activity described above.
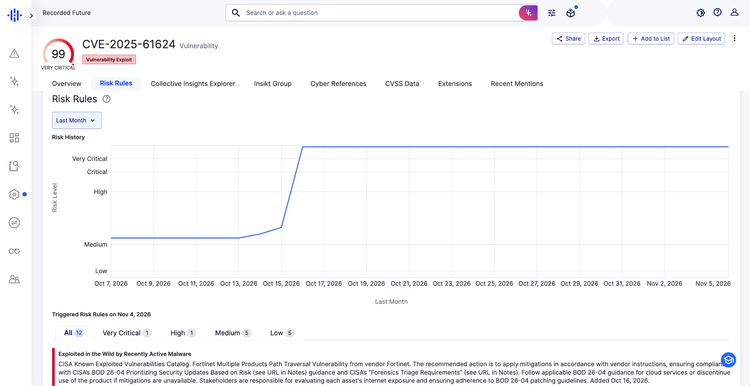
A Validated Intelligence Event linked CL-STA-0954 to exploitation of CVE-2024-47575 (FortiManager) and CVE-2025-61624 (FortiOS). Unit 42 reported command execution, theft of sensitive data associated with more than 500 managed FortiGate firewalls, traffic interception, and deployment of PEERSTITCH.
Additional trends and analyses from October are available to Recorded Future customers.
行動を起こす
環境やベンダー、サプライヤーの脆弱性に関するタイムリーかつ関連性の高い情報は、リスク軽減に不可欠です。Recorded Futureがチームの可視性向上、効率向上、自信に満ちた意思決定を可能にすることで、どのようにサポートできるかをご覧ください。
脆弱性 優先順位付け – 脆弱性は悪用の可能性に基づく 脆弱性 – 単なる深刻さではなく、 悪用されるリスクとその深刻度を容易に把握でき、リアルタイムの状況に応じたインテリジェンスを活用することで、迅速かつ自信を持って意思決定を行い、重要な箇所にパッチを適用し、攻撃を未然に防ぐことができます。
Attack Surface Intelligence – 特定のCVEに対して脆弱なインターネット関連資産を特定します。Attack Surface Intelligence 組織の外部から視点を提供し、未知の資産、脆弱性、または誤った設定の資産を積極的に発見し、優先順位を付ける、対応するのに役立ちます。
サードパーティリスク – ベンダーやパートナーのセキュリティポスチャーを外部から把握しましょう。 インターネット対応システムの脆弱性を迅速に評価できる能力により、時間のかかる調査やベンダーとの連絡サイクルを排除しましょう。
Insikt Group® – Recorded Futureの専門家チームであるInsiktグループ®による新たな脆弱性やトレンドに関する独占レポートにアクセスできます。Insikt Group®が作成した、特定のCVEに対応したNucleiテンプレートをダウンロードして、実際に悪用されている脆弱性を検出してください。
Recorded Future Professional Services – Work with our Professional Services team on a Vulnerability Analysis Engagement. Designed to equip your team with advanced strategies for identifying, prioritizing, and mitigating threats effectively, this program delves into technologies and operations essential for a successful vulnerability management program. (Learn more about how our Professional Services team can help elevate your team by watching our recent Vulnerability Prioritization Workshop.)
Insikt Group®について
Recorded Future の脅威リサーチ部門である Insikt Group は、政府、法執行機関、軍、諜報機関に深い経験を持つアナリストとセキュリティ研究者で構成されています。彼らの使命は、お客様のリスクを軽減し、具体的な成果を実現し、ビジネスの中断を防ぐインテリジェンスを生み出すことです。
関連リソース
サイバーセキュリティ戦略を強化するための専門家の洞察、レポート、ツールをご覧ください。